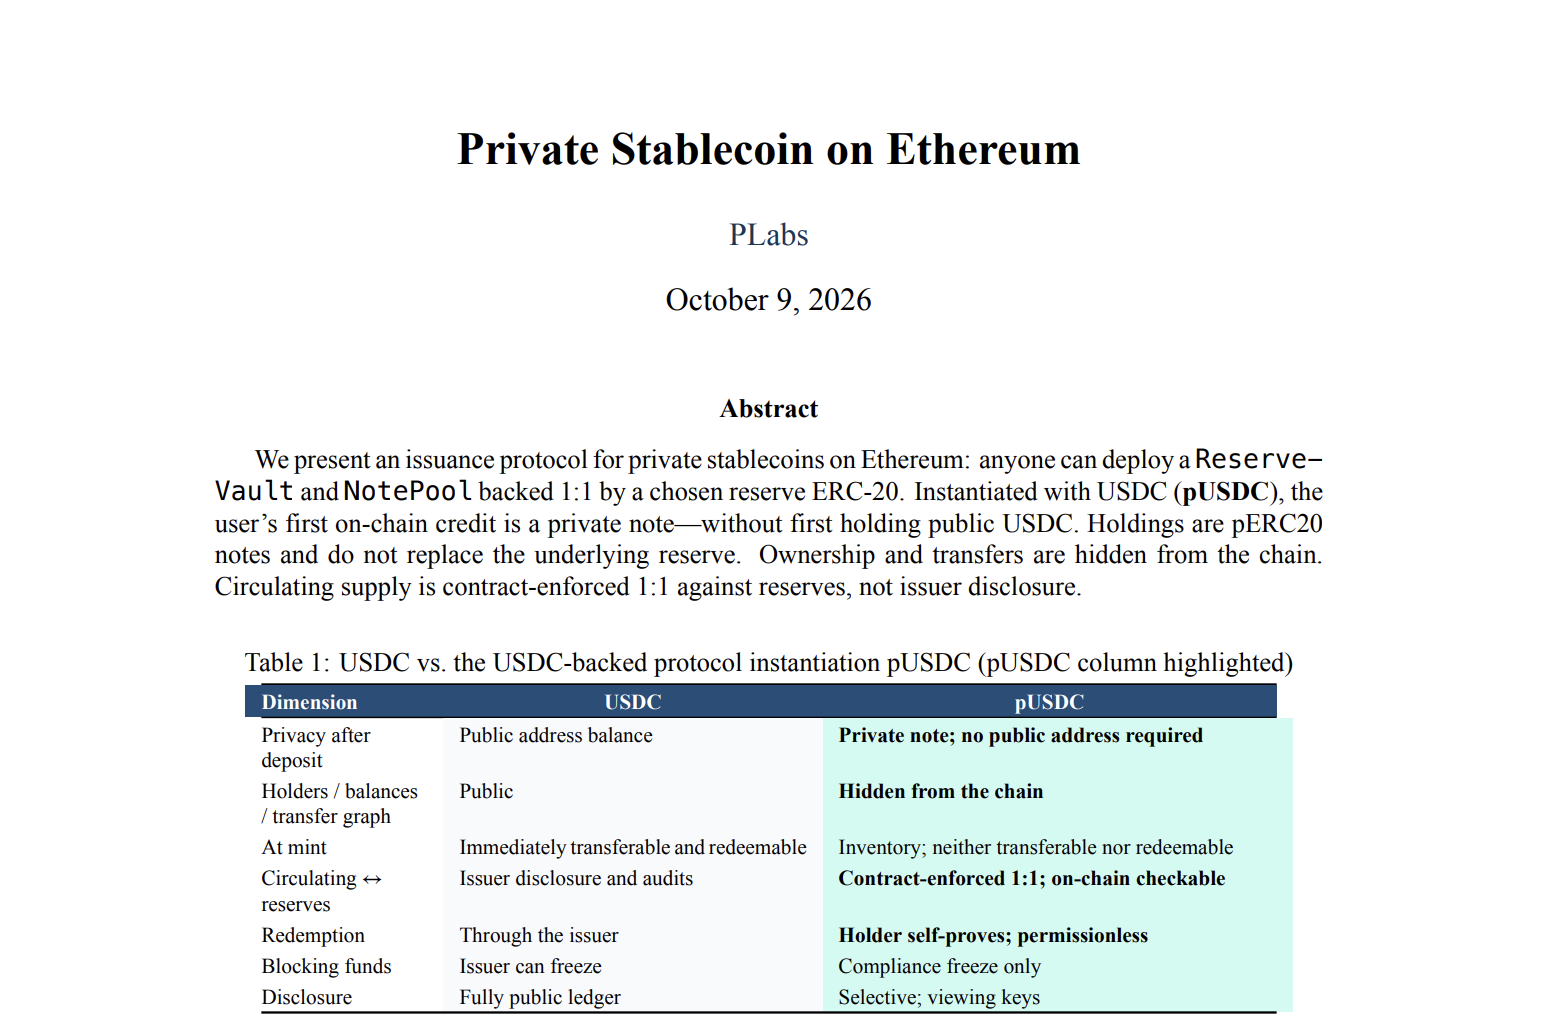
Ethereum’s programmability makes it possible to issue stablecoins with built-in privacy backed by USDC/USDT. A privacy stablecoin protocol on Ethereum can offer:
- Trustless issuance: minting and redemption are enforced by smart contracts rather than by an intermediary.
- Permissionless issuance: anyone can mint and redeem under transparent, on-chain rules, with no gatekeeper.
- DeFi composability: the asset plugs directly into the existing ecosystem of lending, trading, and other on-chain protocols.
- Private or anonymous transactions: transaction data stays confidential or unlinkable to identities.
- Native private DeFi applications: developers can build applications on top of the asset with privacy designed in from the start, rather than bolted on afterward.
Taken together, these properties give privacy stablecoins the potential to become, like stablecoins today, a core building block of the on-chain financial system.
They also open up a new design space for on-chain finance:
- Confidential trading strategies: participants can execute strategies without exposing them to copycats, front-runners, or adversarial observers.
- Selective disclosure: users can prove specific facts about their transactions or holdings (for example, to a counterparty, auditor, or regulator) without revealing everything.
- A new model of social trading: building on selective disclosure, traders can verifiably share their performance or positions with chosen audiences, enabling copy trading and reputation systems without full public exposure.
- Private prediction markets: participants can express views and take positions without revealing their identities or intentions, among other emerging use cases.